PRODUCTION INTEGRATION · PRAYWITHME.FAITH
A safer AI provider boundary for Prayer Companion
PrayWithMe.faith routes its AI-assisted Prayer Companion through ProviderDock so provider credentials, usage controls, routing, and future provider choices remain outside the ministry application.
THE CHALLENGE
Protect a sensitive ministry experience from provider complexity
A direct provider integration puts credential handling, provider-specific errors, metering, and migration work inside the PrayWithMe.faith codebase. Prayer text is sensitive, so the ministry also needs a clear operational boundary that does not retain prompt or response content.
THE APPROACH
Keep the Prayer Companion route and move infrastructure behind it
- A dedicated production tenant isolates credentials and usage.
- The OpenAI key is validated and envelope-encrypted in ProviderDock.
- A server-only token with
gateway:invokereplaces direct provider credentials. - The existing endpoint and ministry safeguards remain unchanged.
- Operational records exclude prayer prompts and generated responses.
THE EXPERIENCE
Prayer Companion stays focused on prayer
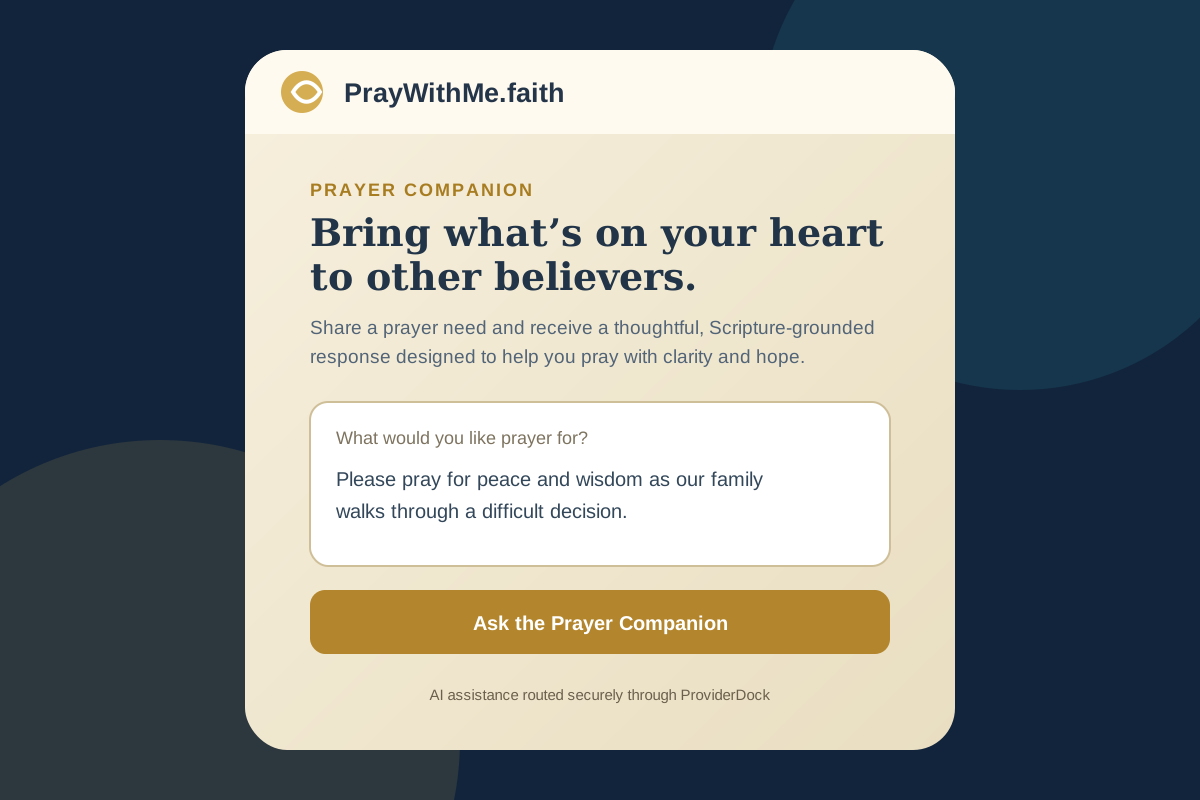
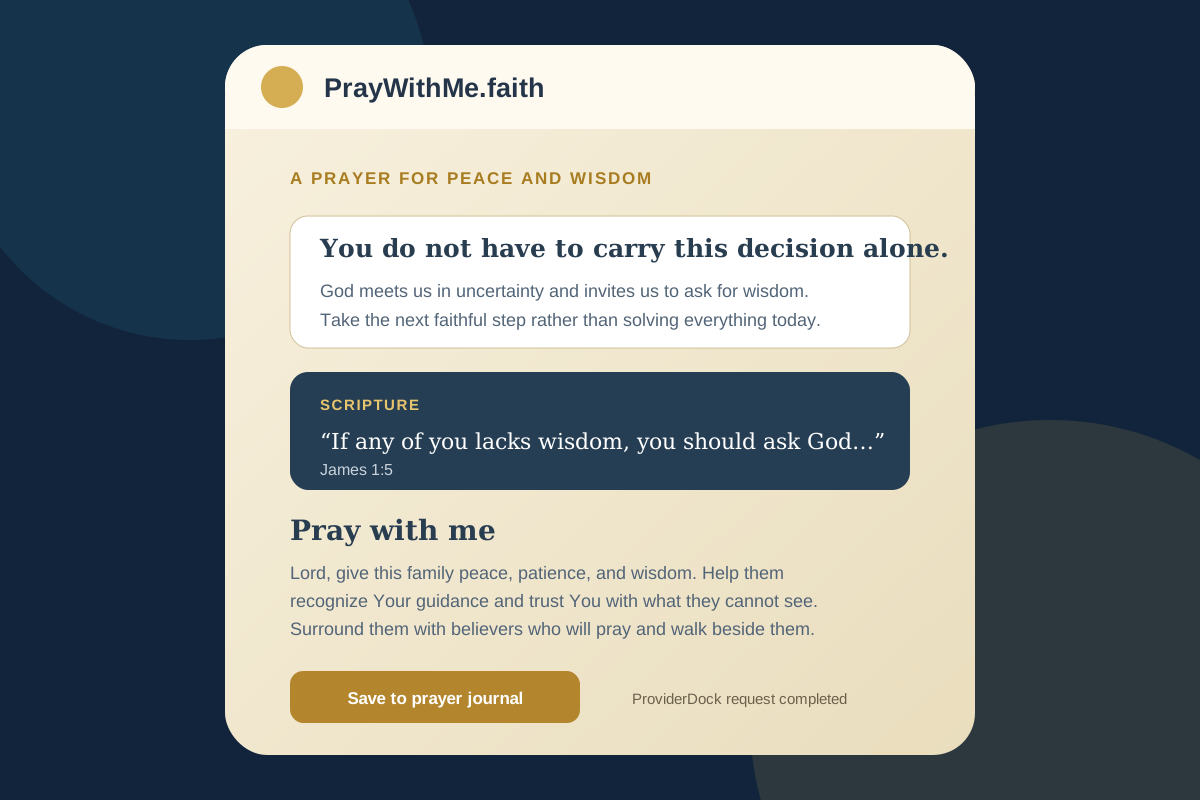
These representative production screens show the request and response flow. ProviderDock works behind the server endpoint, so visitors never see provider infrastructure or credentials.
THE OUTCOME
A production boundary built for reliability and change
The integration centralizes provider operations without redesigning the Prayer Companion experience.
See the implementation details
Review the tenant, SDK, server-route, and production-validation steps used by PrayWithMe.faith.